CMMC Level 2 CNC Machining: What It Means for Defense Programs and Supplier Selection
Borg Design has successfully achieved CMMC Level 2 certification following an assessment by an accredited C3PAO. This milestone reflects more than a compliance requirement—it represents a measurable advancement in how controlled information is protected and how defense-related work is supported across the organization. For defense procurement teams, program managers, and manufacturing engineers, CMMC Level 2 CNC machining is not just about certification. It is about ensuring that suppliers can handle Controlled Unclassified Information (CUI) securely while maintaining the precision, responsiveness, and repeatability required in high-consequence programs.
What CMMC Level 2 Means in CNC Machining
The Cybersecurity Maturity Model Certification (CMMC) Level 2 is a Department of Defense framework designed to ensure that contractors adequately protect Controlled Unclassified Information. It aligns with the requirements outlined in NIST SP 800-171 Rev. 2 and focuses on safeguarding sensitive defense-related data across systems and processes. In a CNC machining environment, this goes beyond IT systems. It affects how technical data is received, stored, accessed, and shared. Drawings, models, specifications, and program details must all be handled with strict controls to prevent unauthorized access or exposure. Achieving CMMC Level 2 confirms that these controls are in place and that they have been validated through an independent assessment.
 Why CMMC Level 2 Matters to Defense Buyers

For defense procurement and program teams, supplier risk is not limited to machining capability. It also includes the ability to securely manage sensitive information throughout the lifecycle of a program. Without proper controls, even a technically capable supplier can introduce risk. Data exposure, inconsistent processes, or gaps in cybersecurity discipline can impact program integrity and compliance. CMMC Level 2 helps reduce that risk by ensuring that suppliers meet a defined standard for protecting CUI. It provides a level of confidence that the supplier’s internal processes align with DoD expectations.
What CMMC Certification Does and Does Not Guarantee
It is important to understand what certification represents in practice. CMMC Level 2 confirms that a supplier has implemented and maintains cybersecurity controls aligned with NIST SP 800-171. It demonstrates that systems, processes, and personnel follow defined practices for protecting controlled information. However, certification alone does not guarantee overall supplier performance. It does not replace the need to evaluate machining capability, engineering support, quality systems, or production reliability. Buyers still need to assess whether a supplier can meet the technical and operational demands of their specific program. In other words, CMMC Level 2 is a critical component of supplier qualification, but it must be considered alongside precision, repeatability, and execution capability.
How Controlled Work Changes Supplier Expectations
Working with Controlled Unclassified Information introduces additional expectations for both suppliers and customers. Communication processes become more structured, data handling procedures are more tightly controlled, and access to information is limited to authorized personnel. These requirements can affect how quickly information is shared, how revisions are managed, and how collaboration takes place between engineering teams and the machine shop. Suppliers that are not prepared for these conditions often struggle to maintain efficiency while meeting compliance requirements. Suppliers that have successfully implemented CMMC-aligned processes are better positioned to operate within these constraints without slowing down program execution.
What Buyers Should Ask About CMMC and Controlled Work
When evaluating a supplier for defense-related machining, certification should be the starting point, not the endpoint. Buyers should seek to understand how cybersecurity practices are integrated into day-to-day operations. Questions should focus on how controlled data is managed throughout the workflow, how access is controlled, and how the supplier maintains both security and responsiveness. It is also important to understand how the supplier supports engineering collaboration under these constraints and how they handle changes during production. These discussions provide a clearer picture of whether the supplier can operate effectively in a controlled environment.
Buyer Impact: Why This Matters Across Teams
Procurement Impact
- CMMC Level 2 certification reduces supplier risk by ensuring that controlled data is handled according to established standards. This supports more confident sourcing decisions and reduces the likelihood of compliance-related disruptions.
Program Management Impact
- Programs that involve controlled work depend on suppliers that can operate within strict requirements without introducing delays. A supplier with validated cybersecurity practices is better equipped to support consistent execution and protect program timelines.
Engineering Impact
- Engineers working with sensitive designs need confidence that their data will be handled securely. At the same time, they need a supplier that can maintain clear communication and support technical collaboration within those constraints.
How Borg Design Supports CMMC Level 2 CNC Machining
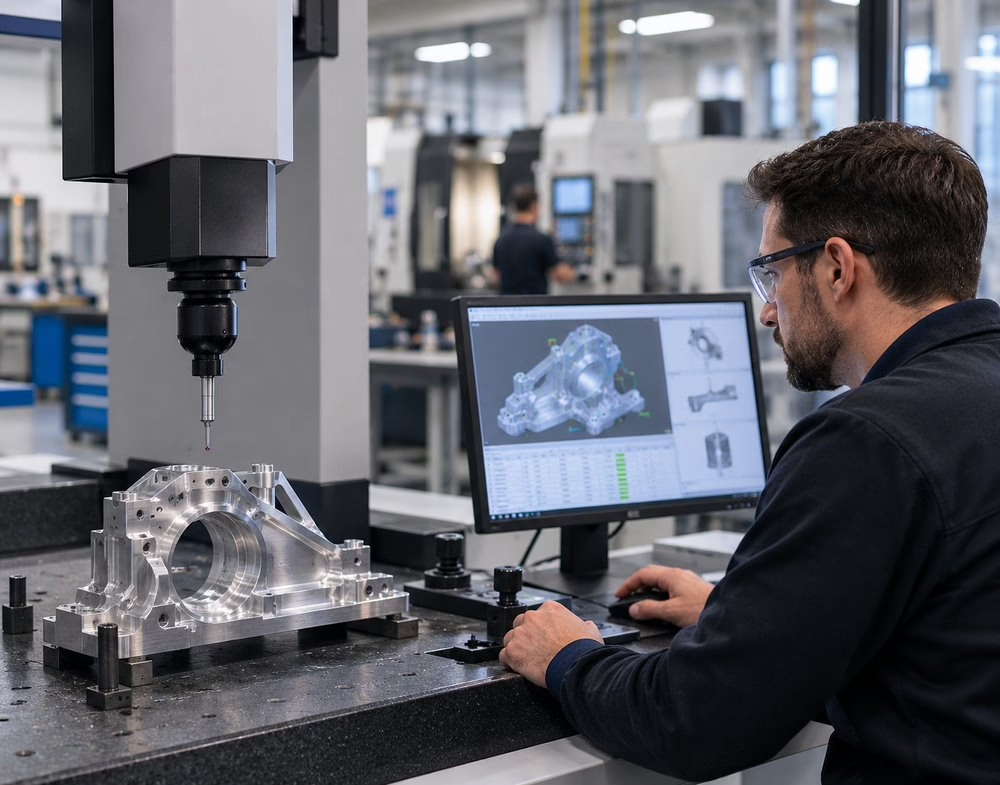
Borg Design’s successful CMMC Level 2 assessment, performed by an accredited C3PAO, reflects a focused effort to strengthen cybersecurity practices and align internal processes with DoD expectations. This includes the protection of Controlled Unclassified Information in accordance with NIST SP 800-171 Rev. 2. In addition to cybersecurity readiness, Borg Design provides precision CNC machining capabilities including milling and turning, tight-tolerance machining, and support for both high-mix low-volume work and production runs. Secondary processes such as passivation, anodizing, plating, heat treatment, and part marking are supported through trusted partners. By combining secure data handling with precision manufacturing capability, Borg Design helps customers meet both compliance and production requirements within defense programs.
Here’s the bottom line.
CMMC Level 2 CNC machining is about more than certification. It reflects a supplier’s ability to protect controlled information while delivering the precision, consistency, and responsiveness required in defense work. For procurement, program, and engineering teams, it is a critical factor in reducing risk and ensuring successful execution.
Request a quote, discuss your defense or controlled work requirements, or connect with our team to review how we support secure, precision CNC machining for high-consequence programs.
FAQs
What is CMMC Level 2 in CNC machining?
- CMMC Level 2 is a cybersecurity certification aligned with NIST SP 800-171 that ensures suppliers can protect Controlled Unclassified Information in defense-related work.
Why is CMMC Level 2 important for defense suppliers?
- It confirms that a supplier has implemented validated cybersecurity practices to safeguard sensitive data required by the Department of Defense.
Does CMMC certification guarantee machining capability?
- No. It ensures cybersecurity compliance, but buyers must still evaluate machining precision, repeatability, and production capability.
What is Controlled Unclassified Information (CUI)?
- CUI is sensitive information used in defense programs that must be protected from unauthorized access, even though it is not classified.
How does CMMC Level 2 affect supplier selection?
- It reduces risk by confirming that a supplier can securely manage controlled data, making them more suitable for defense-related contracts.